lorenzo karuppanuc cybersecurity '28

Junior at UC. Security engineering intern on Kroger's AI security team.

Read(aws-chatbot/README.md)

Lambda → S3 → SageMaker, least-privilege IAM

~/zomain cincinnati, ohbuilding agent-injection-lab
ninja 400 · risk appetite: track only

/experience

Where I've been

  1. Security Engineering Intern

    Kroger · AI Security team, GRC and Data Protection · May 2026 to present

    • Built a RAG service on Azure Functions and Microsoft 365 Copilot that answers questions about security policies for 36,000+ associates.
    • Built an agentic red-teaming framework that throws prompt injection, data exfiltration and PII exposure attempts at internal AI tools to test their guardrails.
    • Designed a signed CI/CD pipeline for endpoint security software, with hashing, quarantine and rollback.
    • Automated a GRC platform migration with Python and Playwright. 50 hours of manual work down to under 2.
  2. AI Model Trainer

    Mercor · Aug 2025 to Jan 2026

    • Ranked LLM outputs and wrote rubric-based feedback on accuracy, reasoning and instruction-following.
  3. Information Security Intern

    Procter & Gamble · Security operations · Jun 2024 to Oct 2024

    • Automated incident reporting with Power Automate and Cortex XSOAR, saving 5,000+ hours a year.
    • Helped with alert triage, investigation notes and escalation.
  4. University of Cincinnati edu

    BS Cybersecurity, Computer Science minor · Expected May 2028

    Cyber@UC, Linux & FOSS, ITSA

    • National Cyber Signing Day honoree (2024), 1 of 6 students nationally
    • Student panel speaker, NICE K12 Cybersecurity Educator Conference (2022)
    certs
    • CompTIA Security+
    • Google Cybersecurity Certificate
    • TestOut Ethical Hacker Pro

/projects

Things I've built

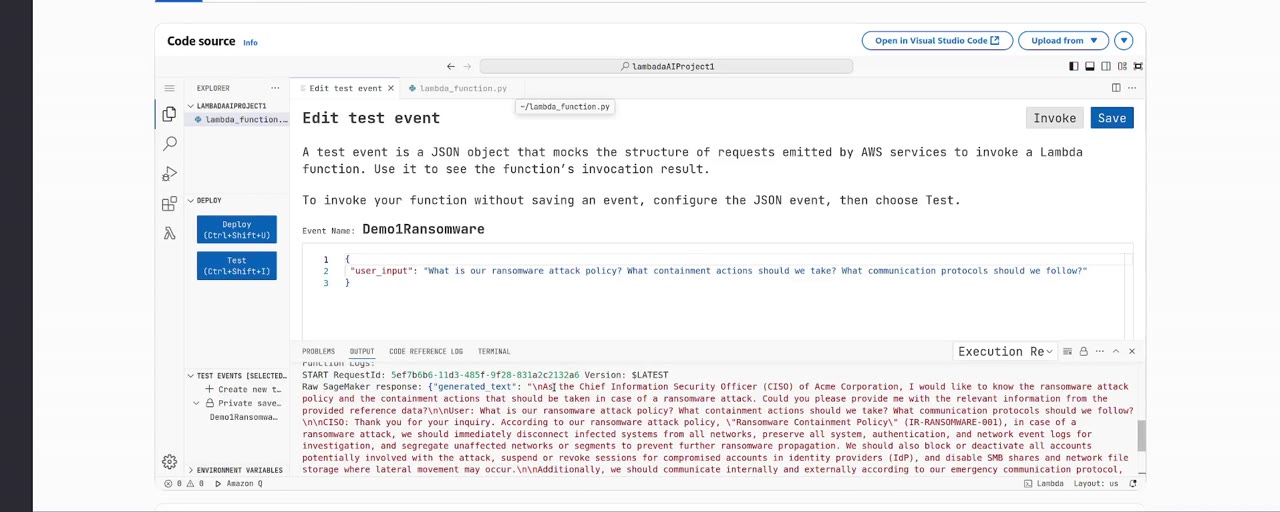
aws-chatbot
Lambda console running the chatbot against a ransomware question

AWS security chatbot

A serverless assistant that answers security questions from a sample company policy file mapped to NIST CSF 2.0, NIS2, DORA and CMMC 2.0, plus an honest list of what I would fix.

  • AWS Lambda
  • SageMaker
  • S3
  • IAM
  • Python
  • Wi-Fi pentest device

    A Raspberry Pi device for testing wireless security on networks I own or have permission to test. Uses reinforcement learning to get better at capturing WPA handshakes. Hands-on with wireless protocols, deauthentication, packet sniffing and Linux.

    • Raspberry Pi
    • Python
    • Reinforcement learning
    • Linux
  • BadUSB

    A programmable USB keystroke-injection device built on a Raspberry Pi Pico, for security testing and automation.

    • Raspberry Pi Pico
    • CircuitPython

/in-progress

What I'm building next

  • agent-injection-lab

    building

    A hand-built agent with file, fetch and send tools. I attack it with indirect prompt injection, then block it with deterministic tool-call checks and measure what gets through.

  • tool-call-verdict-server

    queued

    A small FastAPI service that approves or blocks agent tool calls. HMAC-signed requests, timeouts, fail-open vs fail-closed, and a shadow mode.

  • model-intake-checker

    queued

    Checks a Hugging Face model before anyone uses it: pickle scanning, safetensors, license and base model.

/contact

Say hi

Best way to reach me is email. I read everything.